01 · Operational Capability
One independent practice. Four capability families.
The starting point may be an intrusion, a hostile actor, a disputed claim, a board decision, or a sensitive system that must be built and secured. The disciplines combine when required.
01
Cyber Operations & Digital Forensics
Authorized red teaming and adversary simulation. Incident response, DFIR, threat hunting, breach scoping, malware triage, and cloud, endpoint, identity, and attack-surface assessment.
Cyber operations →
02
Open-Source Intelligence & Technical Investigations
OSINT, digital footprint mapping, threat intelligence, corporate and transaction research, attribution support, and public-source evidence development for technical disputes.
Intelligence & investigations →
03
Private AI & Infrastructure
Local and air-gapped AI on customer-controlled hardware: models, inference, private RAG, integration, isolation, hardening, exposure testing, and production validation.
Private AI & infrastructure →
04
Special Situations & Independent Advisory
Cross-disciplinary matters with contested facts or material stakes: independent review, technical due diligence, executive counsel, and signed conclusions.
Special situations →
02 · Start Here
Start with the situation, not a service catalog.
Choose the closest starting point. If the matter crosses several disciplines, that is usually the reason to call.
Incident response, digital forensics, threat hunting, breach scoping, and recovery.
02 You need to know how an authorized adversary could reach what matters.Red teaming, adversary simulation, exposure assessment, and control validation.
03 A threat, footprint, company, or technical claim needs to be mapped.Lawful OSINT, threat intelligence, technical investigation, and attribution support.
04 Sensitive AI must run under your control and still work in production.Hardware, models, inference, RAG, integration, isolation, hardening, and validation.
05 Capital or accountability depends on technical claims nobody independent has tested.Technical due diligence, incident closure review, executive review, and special situations.
03 · Evidence Room
Work you can inspect before we speak.
Client matters are confidential. These public artifacts show how I define evidence, test systems, and write conclusions. Sanitized matter-specific work product is available during qualified diligence, subject to confidentiality and prior-client permission.
Decision standard
Executive Decision Memorandum
An illustrative signed-conclusion format built for the room where a consequential decision gets made.
Forensic evidence
Forensic Parsers Should Fail Closed
A technical standard for evidence-processing software when silence can manufacture an invisible gap.
Private AI
Local AI Deployment Hardening Checklist
Forty concrete checks across inference, RAG, model artifacts, hosts, access, and incident readiness.
Open-source implementation
Tasia
A public tool that reviews private-AI configuration and produces a hardening pack with evidence.
04 · About Joey
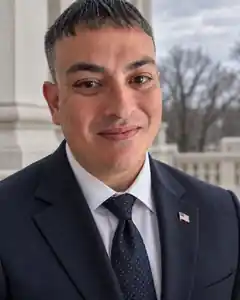
Trained to operate when the facts are incomplete and the consequences are real.
My career began across clinical work and technology. I hold a B.S. in Biology (pre-medical curriculum) from the University of Texas–Pan American and a Specialist Degree in General Medicine (physician qualification) from Novosibirsk State University, including a clinical internship at the E.N. Meshalkin Research Institute. From 2011 to 2014, I worked in clinical research and as a medical scribe across ICU, cardiac-care, and 24-hour emergency-department settings at a 500-bed regional hospital, writing the permanent medical record in real time under HIPAA. That physician training still shapes how I preserve evidence, test hypotheses, and communicate consequences under pressure.
My cybersecurity career spans NCC Group, IBM X-Force IRIS, Microsoft DART, CrowdStrike, and Donorbox. I performed digital forensics, incident response, security testing, and acquisition-related technical examination at NCC Group; led high-severity investigations at IBM; responded to enterprise compromises with Microsoft DART; and advised global clients on cloud security at CrowdStrike. As Director, Information Security & Compliance at Donorbox, I built and led security and compliance for a platform serving more than 50,000 nonprofits, including SOC 2 Type II, PCI DSS Level 1, and a vulnerability disclosure program. Today I am co-founder and VP, Infrastructure & Security at Qompute AI, building and securing private and sovereign AI infrastructure while concurrently leading this independent practice.
Across both disciplines, the method is consistent: stabilize, preserve evidence, test hypotheses, identify irreversible decisions, and turn findings into action. I personally lead from brief through conclusion.
I am direct about conclusions and collaborative with the people who know the system best.
Education & professional credentials
M.S. in Cybersecurity and Information Assurance from Western Governors University. Specialist Degree in General Medicine (physician qualification) from Novosibirsk State University, with a clinical internship at the E.N. Meshalkin Research Institute. B.S. in Biology (pre-medical curriculum) from the University of Texas–Pan American. CISSP, ten GIAC technical certifications, and GIAC Advisory Board recognition, spanning incident response, intrusion analysis, malware reverse engineering, host and network forensics, detection, mobile forensics, and Windows security. Fluent in English, Spanish, and Russian with professional Italian and limited Japanese.
CISSP
Certified Information Systems Security Professional
GSEC
GIAC Security Essentials
GCIH
GIAC Certified Incident Handler
GCIA
GIAC Certified Intrusion Analyst
GREM
GIAC Reverse Engineering Malware
GCFA
GIAC Certified Forensic Analyst
GNFA
GIAC Network Forensic Analyst
GCFE
GIAC Certified Forensic Examiner
GASF
GIAC Advanced Smartphone Forensics
GCDA
GIAC Certified Detection Analyst
GCWN
GIAC Certified Windows Security Administrator
GIAC Advisory Board
GIAC Advisory Board Recognition
Additional certification history includes AWS Certified Cloud Practitioner; Cisco Certified Network Associate Routing and Switching; Cisco Certified Network Associate Security; CompTIA A+; CompTIA Linux+ (Powered by LPI); and CompTIA Security+. Some earlier vendor credentials are no longer active. Issue and expiration dates are available during qualified diligence.
What colleagues say
One recommendation credits my incident-response work with helping to “get the client on track and on the road to recovery in very short order.”
Incident-response delivery
Another describes me as “very friendly and extremely easy to work with,” while “giving advice when needed from his experience.”
Former technical colleague
Excerpts from public LinkedIn recommendations. Names and organizations are omitted on this site.
05 · Independence
Independence is not a disclaimer here. It is the product.
I am not paid to recommend more hardware, close an acquisition, defend a prior thesis, or make an architecture more complex. My economics do not depend on a particular conclusion.
Excellent people can have different incentives, information, and perspectives. Consequential decisions sometimes deserve an independent test.
Any material conflict or commercial affiliation, including my role at Qompute AI, is disclosed before I accept an engagement. Where independence cannot reasonably be preserved, I decline the work.
06 · Operating Model
One accountable principal. Scope that stays honest.
This is a principal-led practice for bounded mandates. The premium is direct accountability, not the pretense of a one-person security operations center.
Personally led
I remain accountable from first brief through final conclusion. Authority, evidence standard, scope, and deliverable are agreed before work begins.
Collaborative with internal teams
The people who know the system contribute context, test hypotheses, and see how evidence changes the working view.
Capacity and specialist requirements disclosed
If a matter needs continuous coverage, a larger team, or a regulated capability outside my scope, I disclose that and structure approved support or decline.
Conflicts addressed before scope
My Qompute AI role and any potential benefit from a recommendation are disclosed in writing before a private-AI scope.
07 · How It Works
Four steps. Clear from the start.
Confidential brief
You tell me the decision, the deadline, and what failure costs. NDA first if you prefer.
Diagnosis
I separate fact from inference, evidence from assumption, and material unknowns from noise. If I am the wrong person, I say so.
Scope & engagement
Scope, authority, evidence standard, and deliverable are agreed in writing. Then claims are tested and evidence preserved.
Evidence & recommendation
A signed conclusion with its supporting evidence, written for the people responsible for the decision.
Proceed
Do not proceed
Proceed only if…
More evidence required
What the deliverable looks like: read an illustrative sample memorandum.
Standing advisory
For leaders who face these decisions repeatedly, fractional CISO / standing independent advisory provides a direct line for second opinions, architecture and vendor review, board preparation, and incident escalation. I accept at most two standing relationships.
08 · Field Notes
Written judgment, published in the open.
Selected writing on incident closure, technical diligence, and private AI custody.
The Incident Is Contained. That Does Not Mean It Is Closed. ↗
The evidence a board should require before accepting that an incident is over.
Technical Due Diligence Should Test the Investment Thesis, Not Merely the Technology ↗
How to test whether technical facts support the economic bet being priced.
Private AI Is a Custody Model, Not a Hosting Model ↗
Why local hosting creates the opportunity for control, not control itself.
Field Notes, by email
One concise note when I find something worth knowing. No news feed.
09 · Beyond the Work
Serious about the work. Curious about almost everything else.
Away from client matters, I spend time with old computers and vintage interactive media, high-fidelity audio, automotive and aviation engineering, and tennis.
My interests also include American government, political campaigns, public policy, and national security. I am based in Las Vegas and maintain a virtual office in Washington, D.C. I stay engaged with civic, political, and cultural life and enjoy meeting people well outside the usual cybersecurity circle.
If we share an interest, you are building something unusual, or you would simply like to compare notes, you are welcome to reach out. Not every useful conversation begins as an engagement.
01 Retro computing & digital preservation
02 High-fidelity audio & recorded music
03 Automotive & aviation engineering
04 Tennis
05 American government, political campaigns & public policy
06 Washington, D.C. & Las Vegas civic life
10 · Contact
Bring me the difficult problem.
Tell me what is happening, what decision has to be made, when it has to be made, and what failure costs. I will tell you directly whether I am the right person, whether or not we work together. I am available worldwide and will travel wherever a matter requires an on-site presence.
The form is best for a structured brief. Please do not send credentials, privileged material, or sensitive evidence through this form. NDA-first conversations are welcome.